How a Red Team Exposed Vulnerabilities in a Leading Indian Steel Manufacturer
Summarize this blog with :
Intro: A leading Indian steel manufacturer faced a cyber gauntlet when an elite red team simulated an attack, exposing critical vulnerabilities in their digital infrastructure.
In one India’s largest steel companies, a quiet yet crucial battle unfolded—not with business competitors, but against hidden cyber threats. A top Indian steel manufacturer took a bold move by hiring expert hackers to test its cybersecurity defenses. What they discovered could reshape how industries think about their online security.
Unmasking the Digital Enemy
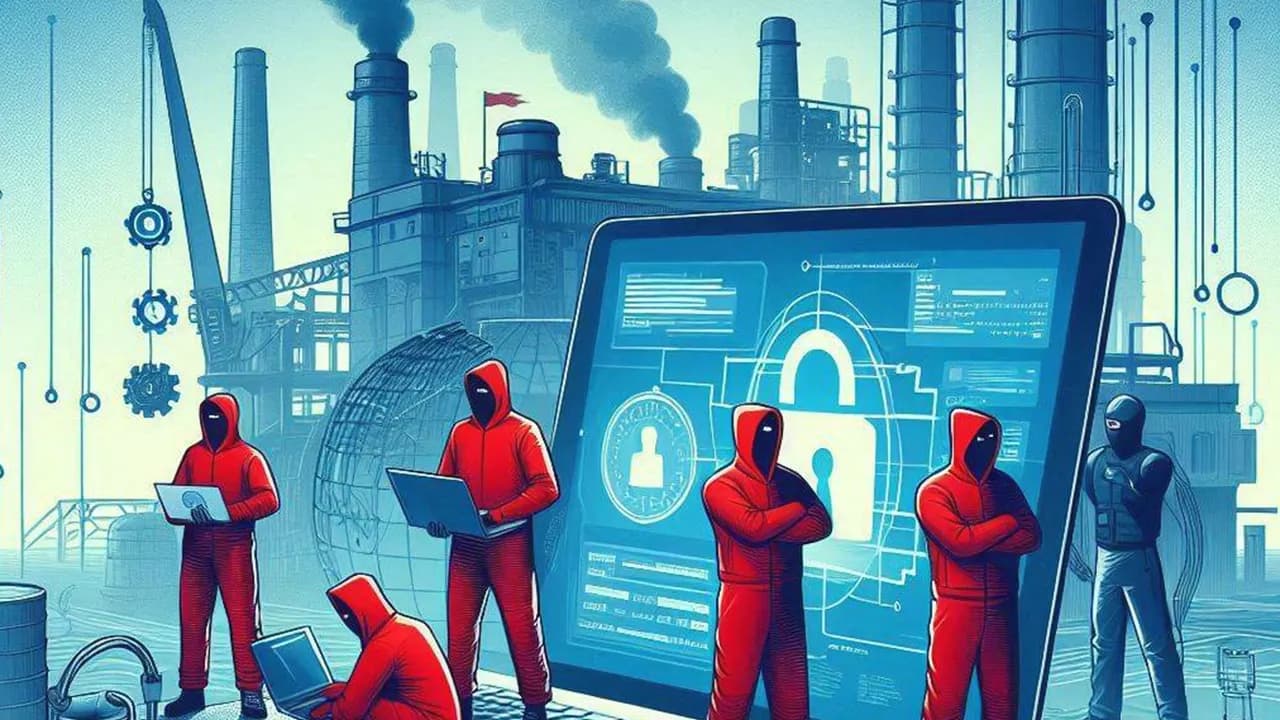
I had a chance to interact with the Red Team—elite cybersecurity experts who were hired to think and act like the enemy. Their mission was both audacious and simple: simulate a cyber-attack with the goal of executing an unauthorized financial transaction. No internal access, no insider knowledge. Just pure external probing and sophisticated hacking techniques.
“We were tasked to test the company’s mettle, but this wasn’t about brute force. It was about strategy, patience, and precision,” says, the lead hacker of the Red Team. “Our job was to think like the bad guys and find a way in without triggering alarms.”
Cracking the Fortress: The Infiltration Begins
Step 1: Vulnerability Search
The operation started with a meticulous sweep of the steel manufacturer's internet-facing systems. “We began by mapping their digital footprint,” the Red Teamer explains. “Every open port, every exposed service—it’s like casing a bank before a heist. You look for the weakest link.”
Their probing soon revealed several potential entry points. These were not glaring holes, but subtle cracks in the fortress walls—overlooked patches, misconfigured servers, and outdated software that could be exploited.
Step 2: Lateral Movement
Once inside, the Red Team didn't stop. They moved laterally across the network, silently creeping from system to system. “We had to find the right target—the laptops and desktops of key personnel authorized to conduct transactions,” the team recounts. “These are the gold mines in any company’s digital landscape.”
Accessing these systems required stealth. The Red Team meticulously gathered credentials and digital certificates, effectively building a skeleton key that could unlock the vaults of the company’s financial operations.
Revealing the Cracks: Security Gaps Highlighted
The Red Team's report painted a clear picture: significant security gaps in the company’s payment systems and broader network infrastructure. These weren’t just theoretical weaknesses; they were real, exploitable flaws that could be used to compromise the company's financial stability.
“The vulnerabilities we found were not unique to this company,” notes. “They’re endemic across many industries that have rapidly digitized without sufficiently fortifying their defenses.”
The Aftermath: Strengthening the Defenses
For the steel manufacturer, the exercise was a wake-up call. The findings provided a critical blueprint for shoring up their defenses, from patching software and tightening network controls to re-evaluating the security of their payment systems.
This proactive approach is becoming essential as industries worldwide face an ever-growing barrage of cyber threats. “The digital battlefield is always evolving,” the Red Team reflects. “What’s secure today might be vulnerable tomorrow. Companies need to stay one step ahead.”
Experience Our Solutions in Action
Explore interactive demos and see how 63SATS helps you stay ahead of evolving cyber threats.